Apache2 : mod_md の設定2021/09/07 |
|
[mod_md] をインストールして、Let's Encrypt から取得する SSL/TLS 証明書の 取得/更新 を自動化します。
設定をしたい対象のバーチャルホストごとに設定可能です。
なお、[mod_md] を設定するバーチャルホストは、こちらの SSL/TLS の手動設定は不要です。
また、Let's Encrypt から手動で取得する際と同様、設定をしたい対象のサイトは、インターネット側からアクセス可能である必要があります。
|
|
| [1] | [mod_md] の設定です。 |
|
root@www:~#
vi /etc/apache2/conf-available/acme.conf # 新規作成
MDBaseServer              on
MDCertificateProtocol     ACME
MDCAChallenges            http-01
MDDriveMode               auto
MDPrivateKeys             RSA 2048
MDRenewWindow             33%
MDStoreDir                md
MDCertificateAuthority    https://acme-v02.api.letsencrypt.org/directory
MDCertificateAgreement    https://letsencrypt.org/documents/LE-SA-v1.2-November-15-2017.pdf

<Location "/md-status">
    SetHandler md-status
    Require ip 127.0.0.1 10.0.0.0/24
</Location>

# [MDRenewWindow]
# 証明書を更新するタイミングを指定する
# 指定しない場合のデフォルトは [33%]
# Let's Encrypt の有効期限 = 90日
# 90日 * 33% ≒ 30日 ⇒ 残り30日で更新される
# 日数で指定する場合の記号は [d]
# 30日 ⇒ [30d]

# [MDStoreDir]
# 証明書等の各種データの保存ディレクトリ
# 指定しない場合のデフォルトは [md]
# [ServerRoot] からの相対パス

# [md-status]
# MD の状態をモニタリングする
|
| [2] | 対象のバーチャルホストごとに設定します。 各 [ServerAdmin] には Let's Encrypt からの各種通知を受け取ることが可能な、有効なメールアドレスを指定する必要があります。 |
MDomain rx-7.srv.world
MDCertificateAgreement accepted
DirectoryIndex index.html
ServerAdmin root@www.srv.world

<VirtualHost *:80>
    DocumentRoot /var/www/rx-7.srv.world
    ServerName rx-7.srv.world
</VirtualHost>

<VirtualHost *:443>
    SSLEngine on
    DocumentRoot /var/www/rx-7.srv.world
    ServerName rx-7.srv.world
</VirtualHost>
a2enmod md Enabling module md. To activate the new configuration, you need to run: systemctl restart apache2root@www:~# a2enconf acme Enabling conf acme. To activate the new configuration, you need to run: systemctl reload apache2root@www:~# a2ensite rx-7.srv.world Enabling site rx-7.srv.world. To activate the new configuration, you need to run: systemctl reload apache2
root@www:~#
systemctl restart apache2
# 初回起動時は各設定のチェックが実行され # [MDStoreDir] に設定したディレクトリ内に起動のためのダミー証明書が作成される root@www:~# ll /etc/apache2/md/domains/rx-7.srv.world total 20 drwx------ 2 root root 4096 Aug 3 07:22 ./ drwx------ 3 root root 4096 Aug 3 07:22 ../ -rw------- 1 root root 1119 Aug 3 10:49 fallback-cert.pem -rw------- 1 root root 1704 Aug 3 10:49 fallback-privkey.pem -rw------- 1 root root 473 Aug 3 10:49 md.json # 問題なければ正規の証明書が取得される root@www:~# ll /etc/apache2/md/domains/rx-7.srv.world total 28 drwx------ 2 root root 4096 Aug 3 07:23 ./ drwx------ 3 root root 4096 Aug 3 07:23 ../ -rw------- 1 root root 3913 Aug 3 10:50 job.json -rw------- 1 root root 518 Aug 3 10:50 md.json -rw------- 1 root root 1704 Aug 3 10:50 privkey.pem -rw------- 1 root root 5591 Aug 3 10:50 pubcert.pem |
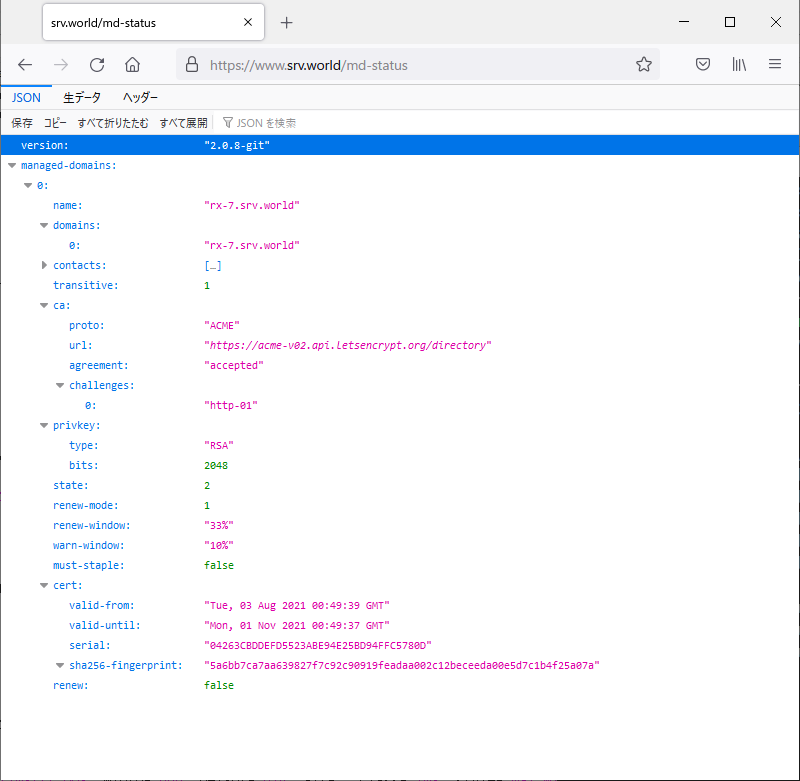
| [3] | 有効期限等々、証明書の確認は [openssl] コマンドで実施可能です。 または、[2] で設定した [md-status] にアクセスすることでも確認できます。 |
|
root@www:~# openssl s_client -connect rx-7.srv.world:443 | openssl x509 -noout -startdate -enddate depth=2 C = US, O = Internet Security Research Group, CN = ISRG Root X1 verify return:1 depth=1 C = US, O = Let's Encrypt, CN = R3 verify return:1 depth=0 CN = rx-7.srv.world verify return:1 notBefore=Aug 3 00:49:39 2021 GMT notAfter=Nov 1 00:49:37 2021 GMT |
|
関連コンテンツ