Elastic Stack 9 : Filebeat インストール2025/08/08 |
|
任意のログファイルのデータ収集機能を提供する Filebeat をインストールします。 |
|
| [1] | Filebeat をインストールします。 事前に Elasticsearch リポジトリ設定済みであることが前提です。 |
|
[root@dlp ~]# dnf -y install filebeat
|
| [2] | 基本的な設定をして Filebeat を起動します。 |
|
[root@dlp ~]#
vi /etc/filebeat/filebeat.yml # 28行目 : 収集するファイルを設定 # ログを収集する場合は enabled: true に変更 # デフォルトは以下のように /var/log/*.log ファイルとなっている # 特定のキーワードを含む行/ファイルを対象/除外にする場合はそれぞれコメント解除して設定
- type: filestream

  # Unique ID among all inputs, an ID is required.
  id: my-filestream-id

  # Change to true to enable this input configuration.
  enabled: true

  # Paths that should be crawled and fetched. Glob based paths.
  paths:
    - /var/log/*.log
    #- c:\programdata\elasticsearch\logs\*

  # Exclude lines. A list of regular expressions to match. It drops the lines that are
  # matching any regular expression from the list.
  # Line filtering happens after the parsers pipeline. If you would like to filter lines
  # before parsers, use include_message parser.
  #exclude_lines: ['^DBG']

  # Include lines. A list of regular expressions to match. It exports the lines that are
  # matching any regular expression from the list.
  # Line filtering happens after the parsers pipeline. If you would like to filter lines
  # before parsers, use include_message parser.
  #include_lines: ['^ERR', '^WARN']

.....
.....
# 137行目 : Kibana を使用する場合はコメント解除して出力先を指定 # Kibana で SSL 有効の場合は証明書に登録したホスト名と合わせる # [username], [password] は管理ユーザーのユーザー名とパスワード # 自己署名の証明書を使用している場合は [ssl.verification_mode: none] setup.kibana: ..... host: "https://dlp.srv.world:5601" protocol: "https" username: "elastic" password: "password" ssl.enabled: true ssl.verification_mode: none # 169行目 : Elasticsearch の出力先を指定する # [username], [password] は管理ユーザーのユーザー名とパスワード # [ssl.certificate_authorities] は Elasticsearch で生成された cacert output.elasticsearch: # Array of hosts to connect to.l hosts: ["https://dlp.srv.world:9200"] protocol: "https" username: "elastic" password: "password" ssl.certificate_authorities: "/etc/elasticsearch/certs/http_ca.crt" ..... .....
[root@dlp ~]#
vi /etc/filebeat/filebeat.reference.yml # 15行目 : 収集する項目を設定
- module: system
  # Syslog
  syslog:
    enabled: true

.....
.....

  # Authorization logs
  auth:
    enabled: true
# 4505行目 : Kibana を使用する場合はコメント解除して出力先を指定 # Kibana で SSL 有効の場合は ssl 系設定をコメント解除 # [username], [password] は管理ユーザーのユーザー名とパスワード # 自己署名の証明書を使用している場合は [ssl.verification_mode: none] setup.kibana: # Kibana Host # Scheme and port can be left out and will be set to the default (http and 5601) # In case you specify and additional path, the scheme is required: http://localhost:5601/path # IPv6 addresses should always be defined as: https://[2001:db8::1]:5601 host: "https://dlp.srv.world:5601" # Optional protocol and basic auth credentials. protocol: "https" username: "elastic" password: "password" # Optional HTTP Path #path: "" # Use SSL settings for HTTPS. Default is true. ssl.enabled: true ..... ..... # after very careful consideration. It is primarily intended as a temporary # diagnostic mechanism when attempting to resolve TLS errors; its use in # production environments is strongly discouraged. # The default value is full. ssl.verification_mode: none[root@dlp ~]# systemctl enable --now filebeat
|
| [3] | データが取り込まれているか確認しておきます。 |
|
# index 一覧 [root@dlp ~]# curl -u elastic --cacert /etc/elasticsearch/certs/http_ca.crt https://127.0.0.1:9200/_cat/indices?v Enter host password for user 'elastic': health status index uuid pri rep docs.count docs.deleted store.size pri.store.size dataset.size ..... ..... yellow open .ds-metricbeat-9.1.0-2025.08.06-000001 0TnJalxZRTC3529MN3X87g 1 1 28 0 107.4kb 107.4kb 107.4kb yellow open .ds-packetbeat-9.1.0-2025.08.06-000001 n0ML1vQsQbm4wQLkO8bprQ 1 1 0 0 227b 227b 227b yellow open .ds-filebeat-9.1.1-2025.08.08-000001 RwMbn1YDSZ-xcm8dTC6clQ 1 1 3200 0 641.5kb 641.5kb 641.5kb # index のドキュメント一覧 [root@dlp ~]# curl -u elastic --cacert /etc/elasticsearch/certs/http_ca.crt https://127.0.0.1:9200/.ds-filebeat-9.1.1-2025.08.08-000001/_search?pretty
Enter host password for user 'elastic':
{
  "took" : 1,
  "timed_out" : false,
  "_shards" : {
    "total" : 1,
    "successful" : 1,
    "skipped" : 0,
    "failed" : 0
  },
  "hits" : {
    "total" : {
      "value" : 3866,
      "relation" : "eq"
    },
    "max_score" : 1.0,
    "hits" : [
      {
        "_index" : ".ds-filebeat-9.1.1-2025.08.08-000001",
        "_id" : "MQIKh5gBzSdMfqv7Jgq-",
        "_score" : 1.0,
        "_source" : {
          "@timestamp" : "2025-08-08T00:17:15.298Z",
          "message" : "2025-08-08T08:50:51+0900 DEBUG baseos: has expired and will be refreshed.",
          "log" : {
            "offset" : 139179,
            "file" : {
              "path" : "/var/log/dnf.log",
              "device_id" : "64768",
              "inode" : "33565389",
              "fingerprint" : "64f8000b6cabea2e37678ad2fe87199ade4f0b10bce270d6cb410f43c6ae2585"
            }
          },
          "input" : {
            "type" : "filestream"
          },
          "host" : {
            "mac" : [
              "52-54-00-48-21-1F",
              "52-54-00-E8-AD-A3"
            ],
            "hostname" : "dlp.srv.world",
            "architecture" : "x86_64",
            "os" : {
              "name" : "CentOS Stream",
              "kernel" : "6.12.0-113.el10.x86_64",
              "codename" : "Coughlan",
              "type" : "linux",
              "platform" : "centos",
              "version" : "10 (Coughlan)",
              "family" : "redhat"
            },
            "name" : "dlp.srv.world",
            "id" : "617bcf1bbafa427a96614dca366f22c7",
            "containerized" : false,
            "ip" : [
              "10.0.0.30",
              "fe80::5054:ff:fee8:ada3"
            ]
          },
.....
.....
|
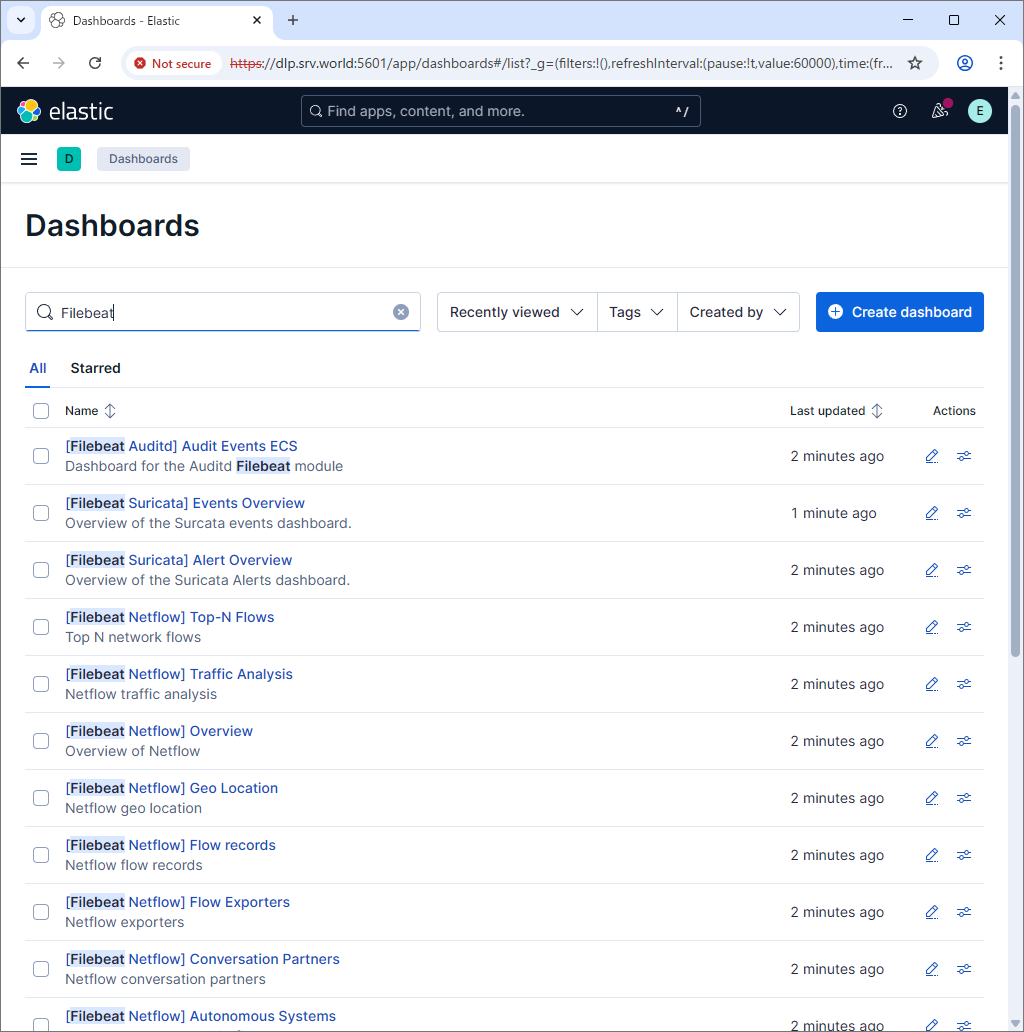
| [4] | Kibana を稼働させている場合は、データインポートが可能です。 |
|
[root@dlp ~]# filebeat setup --dashboards Loading dashboards (Kibana must be running and reachable) Loaded dashboards |
|
関連コンテンツ