Elastic Stack 8 : Install Filebeat2022/11/09 |
|
Install Filebeat that easily ships log file data to Elasticsearch or Logstash.
|
|
| [1] | Install Filebeat. Configure Elasticsearch repository before it. |
|
root@dlp:~# apt -y install filebeat
|
| [2] | Configure basic settings and start Filebeat. |
|
root@dlp:~#
vi /etc/filebeat/filebeat.yml # line 28 : set items to collect data # if collect logs, turn to [enabled: true] # by default, /var/log/*.log files are shipped
- type: filestream

  # Unique ID among all inputs, an ID is required.
  id: my-filestream-id

  # Change to true to enable this input configuration.
  enabled: true

  # Paths that should be crawled and fetched. Glob based paths.
  paths:
    - /var/log/*.log
    #- c:\programdata\elasticsearch\logs\*

  # Exclude lines. A list of regular expressions to match. It drops the lines that are
  # matching any regular expression from the list.
  # Line filtering happens after the parsers pipeline. If you would like to filter lines
  # before parsers, use include_message parser.
  #exclude_lines: ['^DBG']

  # Include lines. A list of regular expressions to match. It exports the lines that are
  # matching any regular expression from the list.
  # Line filtering happens after the parsers pipeline. If you would like to filter lines
  # before parsers, use include_message parser.
  #include_lines: ['^ERR', '^WARN']

.....
.....
# line 108 : if use Kibana, uncomment and specify output host # if SSL is enabled on Kibana, hostname should be the same with the hostname in certs # [username] and [password] is the admin user's one # if using self-signed certificate, specify [ssl.verification_mode: none] setup.kibana: ..... host: "https://dlp.srv.world:5601" protocol: "https" username: "elastic" password: "password" ssl.enabled: true ssl.verification_mode: none # line 144 : specify output of Elasticsearch # [username] and [password] is the admin user's one # [ssl.certificate_authorities] is the cacert generated by Elasticsearch installation output.elasticsearch: # Array of hosts to connect to.l hosts: ["https://dlp.srv.world:9200"] protocol: "https" username: "elastic" password: "password" ssl.certificate_authorities: "/etc/elasticsearch/certs/http_ca.crt" ..... .....
root@dlp:~#
vi /etc/filebeat/filebeat.reference.yml # line 15 : set items to collect data
- module: system
  # Syslog
  syslog:
    enabled: true

.....
.....

  # Authorization logs
  auth:
    enabled: true
# line 4720 : if use Kibana, uncomment and specify output host # if SSL is enabled on Kibana, uncomment ssl related lines # [username] and [password] is the admin user's one # if using self-signed certificate, specify [ssl.verification_mode: none] setup.kibana: # Kibana Host # Scheme and port can be left out and will be set to the default (http and 5601) # In case you specify and additional path, the scheme is required: http://localhost:5601/path # IPv6 addresses should always be defined as: https://[2001:db8::1]:5601 host: "https://dlp.srv.world:5601" # Optional protocol and basic auth credentials. protocol: "https" username: "elastic" password: "password" # Optional HTTP Path #path: "" # Use SSL settings for HTTPS. Default is true. ssl.enabled: true ..... ..... # after very careful consideration. It is primarily intended as a temporary # diagnostic mechanism when attempting to resolve TLS errors; its use in # production environments is strongly discouraged. # The default value is full. ssl.verification_mode: noneroot@dlp:~# systemctl enable --now filebeat
|
| [3] | Verify status the data has been collected normally. |
|
# index list root@dlp:~# curl -u elastic --cacert /etc/elasticsearch/certs/http_ca.crt https://127.0.0.1:9200/_cat/indices?v Enter host password for user 'elastic': health status index uuid pri rep docs.count docs.deleted store.size pri.store.size yellow open .ds-metricbeat-8.5.0-2022.11.09-000001 MRfmgqLxSGCLapOAJDDZww 1 1 12862 0 15.2mb 15.2mb yellow open .ds-packetbeat-8.5.0-2022.11.09-000001 ooN-ezjvT_-j19g8hmYkwQ 1 1 14229 0 5.5mb 5.5mb yellow open .ds-filebeat-8.5.0-2022.11.09-000001 KNL7VJaXTK-hk7ZVxyty3Q 1 1 6765 0 1mb 1mb yellow open test_index Yw-_PdilSIueIBLM9KmihQ 1 1 1 0 6.4kb 6.4kb # document list on the index root@dlp:~# curl -u elastic --cacert /etc/elasticsearch/certs/http_ca.crt https://127.0.0.1:9200/.ds-filebeat-8.5.0-2022.11.09-000001/_search?pretty
Enter host password for user 'elastic':
{
  "took" : 1,
  "timed_out" : false,
  "_shards" : {
    "total" : 1,
    "successful" : 1,
    "skipped" : 0,
    "failed" : 0
  },
  "hits" : {
    "total" : {
      "value" : 6765,
      "relation" : "eq"
    },
    "max_score" : 1.0,
    "hits" : [
      {
        "_index" : ".ds-filebeat-8.5.0-2022.11.09-000001",
        "_id" : "cFZjW4QBpfPiykRa5VVv",
        "_score" : 1.0,
        "_source" : {
          "@timestamp" : "2022-11-09T07:56:18.231Z",
          "input" : {
            "type" : "filestream"
          },
          "ecs" : {
            "version" : "8.0.0"
          },
          "host" : {
            "name" : "dlp.srv.world",
            "mac" : [
              "52-54-00-97-AA-CC"
            ],
            "hostname" : "dlp.srv.world",
            "architecture" : "x86_64",
            "os" : {
              "platform" : "ubuntu",
              "version" : "22.04.1 LTS (Jammy Jellyfish)",
.....
|
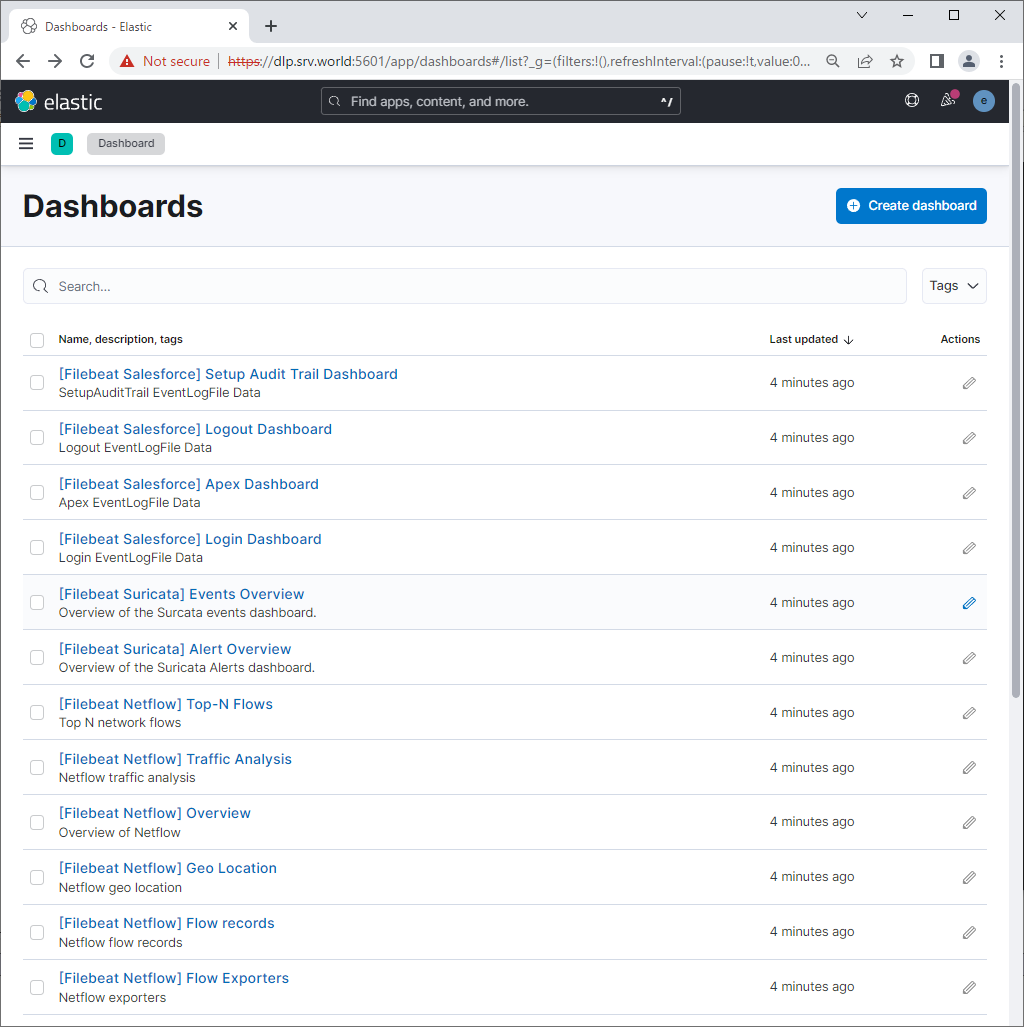
| [4] | If Kibana is running, it's possible to import data to sample Dashboards. |
|
root@dlp:~# filebeat setup --dashboards Loading dashboards (Kibana must be running and reachable) Loaded dashboards |
|
Matched Content