Apache2 : Configure mod_security2025/09/09 |
|
Enable [mod_security] module to configure Web Application Firewall (WAF). |
|
| [1] | Install [mod_security]. |
|
root@www:~# apt -y install libapache2-mod-security2
|
| [2] | Enable [mod_security]. |
|
root@www:~# cp -p /etc/modsecurity/modsecurity.conf-recommended /etc/modsecurity/modsecurity.conf
root@www:~#
vi /etc/modsecurity/modsecurity.conf
    line 7 : [SecRuleEngine DetectionOnly] is set as default, it does not block actions
    # if you'd like to block actions, change to [SecRuleEngine On]
    SecRuleEngine DetectionOnly
.....
.....
|
| [3] |
It's possible to write a rule like follows. ⇒ SecRule VARIABLES OPERATOR [ACTIONS]
Each parameter has many kind of values, refer to official documents below. |
| [4] | For Example, set some rules and verify it works normally. |
|
root@www:~#
vi /etc/modsecurity/localrules.conf # default action when matching rules SecDefaultAction "phase:2,deny,log,status:406" # [etc/passwd] is included in request URI SecRule REQUEST_URI "etc/passwd" "id:'500001'" # [../] is included in request URI SecRule REQUEST_URI "\.\./" "id:'500002'" # [<SCRIPT] is included in arguments SecRule ARGS "<[Ss][Cc][Rr][Ii][Pp][Tt]" "id:'500003'" # [SELECT FROM] is included in arguments SecRule ARGS "[Ss][Ee][Ll][Ee][Cc][Tt][[:space:]]+[Ff][Rr][Oo][Mm]" "id:'500004'" systemctl reload apache2
|
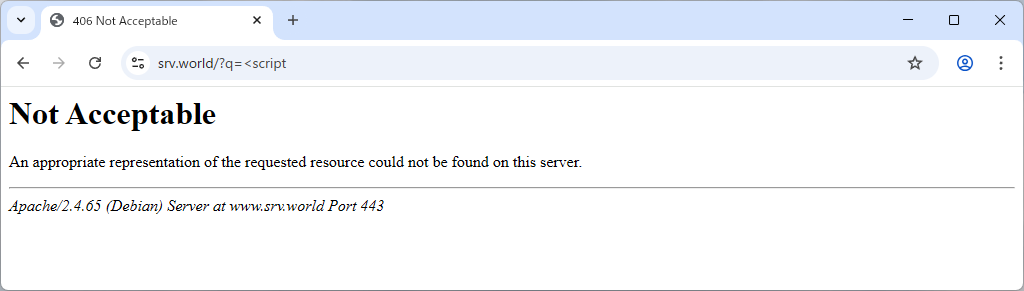
| [5] | Access to the URI which includes words you set and verify it works normally. |
|
| [6] | The logs for [mod_security] is placed in the directory like follows. |
|
root@www:~# cat /var/log/apache2/modsec_audit.log --2bf0551b-H-- Message: Access denied with code 406 (phase 2). Pattern match "<[Ss][Cc][Rr][Ii][Pp][Tt]" at ARGS:q. [file "/etc/modsecurity/localrules.conf"] [line "10"] [id "500003"] Apache-Error: [file "apache2_util.c"] [line 286] [level 3] ModSecurity: Access denied with code 406 (phase 2). Pattern match "<[Ss][Cc][Rr][Ii][Pp][Tt]" at ARGS:q. [file "/etc/modsecurity/localrules.conf"] [line "10"] [id "500003"] [hostname "www.srv.world"] [uri "/"] [unique_id "aL9t-eiqmdJ7OZHpI0MYhAAAAgA"] Action: Intercepted (phase 2) Stopwatch: 1757375993307050 1277 (- - -) Stopwatch2: 1757375993307050 1277; combined=531, p1=437, p2=5, p3=0, p4=0, p5=89, sr=42, sw=0, l=0, gc=0 Response-Body-Transformed: Dechunked Producer: ModSecurity for Apache/2.9.11 (http://www.modsecurity.org/); OWASP_CRS/3.3.7. Server: Apache/2.4.65 (Debian) Engine-Mode: "ENABLED" ..... ..... |
| [7] | General rules are provided and applied by default under the directory below. However maybe you need to customize them for your own web sites not to block necessary requests. |
|
root@www:~# ll /usr/share/modsecurity-crs/rules total 688 -rw-r--r-- 1 root root 786 Nov 1 2024 crawlers-user-agents.data -rw-r--r-- 1 root root 551 Nov 1 2024 iis-errors.data -rw-r--r-- 1 root root 933 Nov 1 2024 java-classes.data -rw-r--r-- 1 root root 264 Nov 1 2024 java-code-leakages.data -rw-r--r-- 1 root root 240 Nov 1 2024 java-errors.data -rw-r--r-- 1 root root 31209 Nov 1 2024 lfi-os-files.data -rw-r--r-- 1 root root 5409 Nov 1 2024 php-config-directives.data -rw-r--r-- 1 root root 9201 Nov 1 2024 php-errors.data -rw-r--r-- 1 root root 683 Nov 1 2024 php-function-names-933150.data -rw-r--r-- 1 root root 21282 Nov 1 2024 php-function-names-933151.data -rw-r--r-- 1 root root 224 Nov 1 2024 php-variables.data -rw-r--r-- 1 root root 13813 Nov 1 2024 REQUEST-901-INITIALIZATION.conf ..... ..... |
Matched Content