Elastic Stack 9 : Install Packetbeat2025/08/08 |
|
Install Packetbeat that collects and analyze Network packets. |
|
| [1] | Install Packetbeat. Configure Elasticsearch repository before it. |
|
[root@dlp ~]# dnf -y install packetbeat
|
| [2] | Configure basic settings and start Packetbeat. |
|
[root@dlp ~]#
vi /etc/packetbeat/packetbeat.yml # line 58 : set items to collect data # if disable ICMPv4/ICMPv6, turn to false # line 44 and later : many items are targeted as monitoring by default, # but if not need, comment out the line [ports: ***] packetbeat.protocols: - type: icmp # Enable ICMPv4 and ICMPv6 monitoring. Default: false enabled: true - type: amqp # Configure the ports where to listen for AMQP traffic. You can disable # the AMQP protocol by commenting out the list of ports. ports: [5672] ..... ..... # line 181 : if use Kibana, uncomment and specify output host # if SSL is enabled on Kibana, hostname should be the same with the hostname in certs # [username] and [password] is the admin user's one # if using self-signed certificate, specify [ssl.verification_mode: none] setup.kibana: ..... host: "https://dlp.srv.world:5601" protocol: "https" username: "elastic" password: "password" ssl.enabled: true ssl.verification_mode: none # line 217 : specify output of Elasticsearch # [username] and [password] is the admin user's one # [ssl.certificate_authorities] is the cacert generated by Elasticsearch installation output.elasticsearch: # Array of hosts to connect to. hosts: ["https://dlp.srv.world:9200"] protocol: "https" username: "elastic" password: "password" ssl.certificate_authorities: "/etc/elasticsearch/certs/http_ca.crt" ..... .....
[root@dlp ~]#
vi /etc/packetbeat/packetbeat.reference.yml # line 1870 : if use Kibana, uncomment and specify output host # if SSL is enabled on Kibana, uncomment ssl related lines # [username] and [password] is the admin user's one # if using self-signed certificate, specify [ssl.verification_mode: none] setup.kibana: # Kibana Host # Scheme and port can be left out and will be set to the default (http and 5601) # In case you specify and additional path, the scheme is required: http://localhost:5601/path # IPv6 addresses should always be defined as: https://[2001:db8::1]:5601 host: "https://dlp.srv.world:5601" # Optional protocol and basic auth credentials. protocol: "https" username: "elastic" password: "password" # Optional HTTP Path #path: "" # Use SSL settings for HTTPS. Default is true. ssl.enabled: true ..... ..... # after very careful consideration. It is primarily intended as a temporary # diagnostic mechanism when attempting to resolve TLS errors; its use in # production environments is strongly discouraged. # The default value is full. ssl.verification_mode: none[root@dlp ~]# systemctl enable --now packetbeat
|
| [3] | Verify status the data has been collected normally. |
|
# index list [root@dlp ~]# curl -u elastic --cacert /etc/elasticsearch/certs/http_ca.crt https://127.0.0.1:9200/_cat/indices?v Enter host password for user 'elastic' health status index uuid pri rep docs.count docs.deleted store.size pri.store.size dataset.size ..... ..... yellow open .ds-metricbeat-9.1.0-2025.08.06-000001 0TnJalxZRTC3529MN3X87g 1 1 28 0 107.4kb 107.4kb 107.4kb yellow open .ds-packetbeat-9.1.1-2025.08.08-000001 ca3CMl83RXGiJGodnrdrBQ 1 1 9 0 46.2kb 46.2kb 46.2kb # document list on the index [root@dlp ~]# curl -u elastic --cacert /etc/elasticsearch/certs/http_ca.crt https://127.0.0.1:9200/.ds-packetbeat-9.1.1-2025.08.08-000001/_search?pretty
Enter host password for user 'elastic':
{
  "took" : 0,
  "timed_out" : false,
  "_shards" : {
    "total" : 1,
    "successful" : 1,
    "skipped" : 0,
    "failed" : 0
  },
  "hits" : {
    "total" : {
      "value" : 207,
      "relation" : "eq"
    },
    "max_score" : 1.0,
    "hits" : [
      {
        "_index" : ".ds-packetbeat-9.1.1-2025.08.08-000001",
        "_id" : "gwEEh5gBzSdMfqv7pvAV",
        "_score" : 1.0,
        "_source" : {
          "server" : {
            "port" : 53,
            "bytes" : 81,
            "ip" : "10.0.0.10"
          },
          "agent" : {
            "name" : "dlp.srv.world",
            "id" : "b45a0ec3-8ddb-450f-944d-b3940b276c3b",
            "type" : "packetbeat",
            "ephemeral_id" : "6c25bbac-9051-4ee8-b296-d881c9079a0e",
            "version" : "9.1.1"
          },
          "method" : "QUERY",
          "resource" : "dlp.srv.world",
          "query" : "class IN, type A, dlp.srv.world",
          "destination" : {
            "port" : 53,
            "bytes" : 81,
            "ip" : "10.0.0.10"
          },
          "dns" : {
            "op_code" : "QUERY",
            "resolved_ip" : [
              "10.0.0.30"
            ],
.....
.....
|
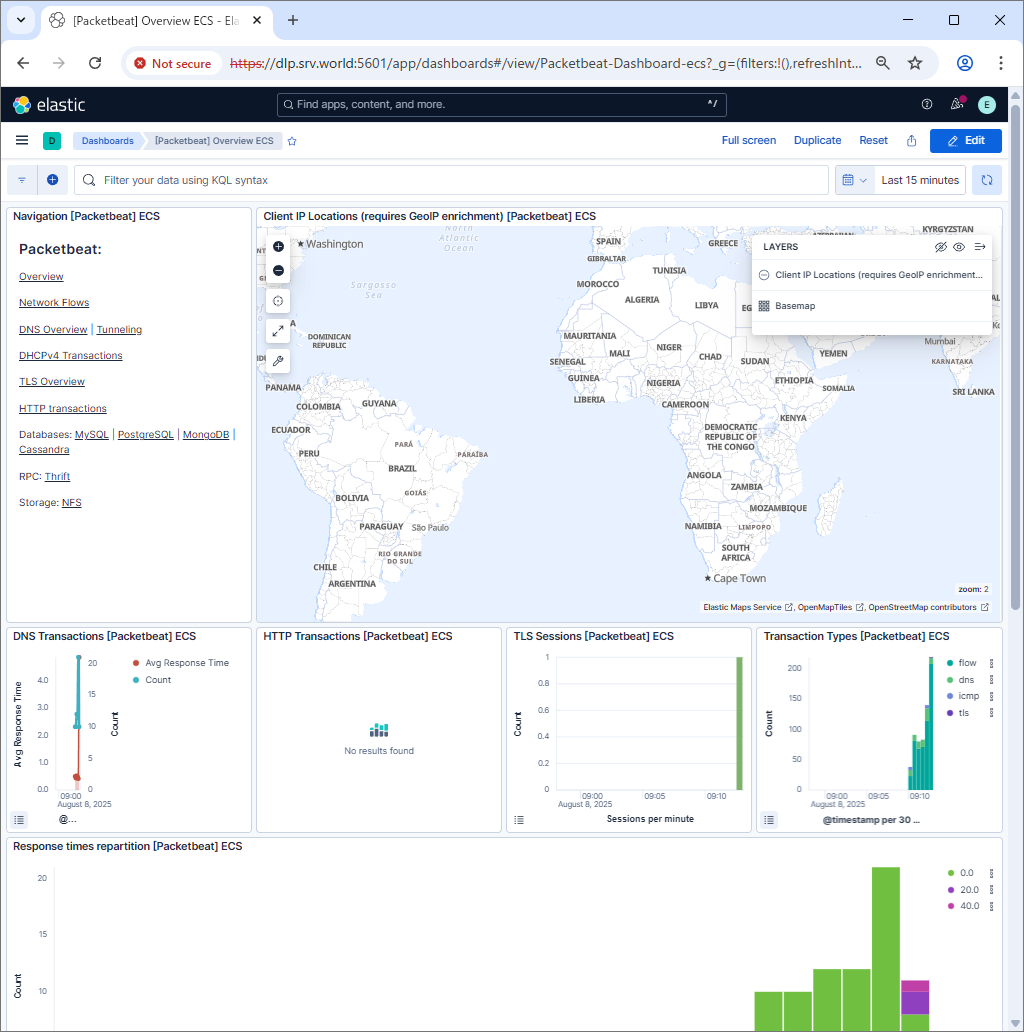
| [4] | If Kibana is running, it's possible to import data to sample Dashboards. |
|
[root@dlp ~]# packetbeat setup --dashboards Loading dashboards (Kibana must be running and reachable) Loaded dashboards |
|
Matched Content